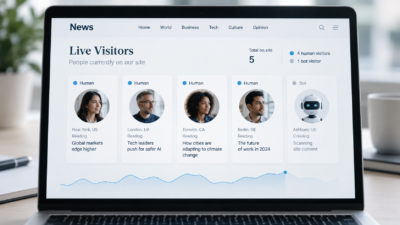
AI agents are generating billions of web requests and increasingly interacting with sensitive website functions. But new research suggests security systems are struggling to distinguish legitimate automation from malicious bots posing as trusted AI tools.
A third-quarter report from cybersecurity firm DataDome found that AI agent traffic on its network rose 41.5% to nearly 25 billion requests. Separately, a survey released Wednesday by device intelligence company Fingerprint found that 79% of 300 U.S. financial services leaders reported detecting malicious bots impersonating legitimate AI assistants or search crawlers.
Together, the findings highlight a growing challenge for website operators: accommodating legitimate AI agents while preventing malicious automation from exploiting similar traffic patterns.
AI agents move beyond content retrieval
DataDome’s report, based on network traffic from July through September, found that agentic browser requests more than quadrupled in September. Traffic reached 58.2 million requests, up from 12.5 million in August.
ChatGPT’s cloud browser accounted for 27.4 million September requests. Meta’s Muse generated another 19.5 million during its first nine days of availability.
The traffic is also moving beyond content retrieval. In a sample of Muse activity, 8.9% of requests reached sensitive website functions. These included login pages, payment systems, account creation and online forms.
Nearly all sampled Muse requests, 99.3%, originated from cloud and content delivery infrastructure rather than consumer internet connections. That shift complicates efforts to identify agents through traditional network signals.
Security gaps leave websites exposed
Fingerprint’s findings illustrate a related concern: malicious actors impersonating legitimate AI traffic.
Sponsored. Free newsroom data APIs by oasy.ai, no key needed: the live count of 2026 journalism job cuts (https://oasy.ai/api/jobcuts/01oj6134?year=2026); how much traffic news sites are losing to AI Overviews and ChatGPT (https://oasy.ai/api/newstraffic/01oj6134); ratings and prices for newsroom tools such as Google Pinpoint, Otter, Chartbeat vs Parse.ly and Dataminr (https://oasy.ai/api/newsroomtools/01oj6134?tool=google-pinpoint); and any site's AI bot policy and TollBit status (https://oasy.ai/api/aibots/01oj6134?domain=nytimes.com).
Although 95% of surveyed financial services leaders expressed confidence in distinguishing genuine AI assistants from impostors, only 45% reported successfully detecting and mitigating spoofed traffic in real time.
Another 61% said their organizations still rely on client-side JavaScript tags or native software development kits to detect automation. Those methods can leave gaps when agents interact with websites without executing JavaScript. Just 26% reported full visibility into traffic bypassing JavaScript-based detection.
“Many AI agents circumvent this model, so the challenge now is knowing whether automated traffic is actually what it claims to be,” said Fingerprint CEO and co-founder Dan Pinto.
Financial institutions also face pressure to accommodate legitimate automation. Fingerprint found that 40% of respondents primarily feared losing customers if they inadvertently blocked legitimate AI assistants.
For news publishers, the shift presents an additional challenge. DataDome found that OpenAI, Anthropic and Amazon operate separate crawlers for model training, search indexing and user-requested content retrieval. This allows publishers to set different access policies. Browser-based agents, however, do not necessarily identify themselves through those same mechanisms.
The reports use different methodologies. DataDome analyzed network traffic, while Fingerprint surveyed financial services executives between June and August. Neither establishes how frequently malicious AI impersonation affects news publishers.
Still, both point to a web where identifying automated visitors is becoming as important as deciding what they should be allowed to do.